Hackers attack websites of every size, and small business sites are no exception. When a site gets infected with malicious code, visitors can unknowingly pick up the malware and pass it on to other people.
Protecting your site starts with two questions: how secure is your website right now, and what can you do to make it safer?
Web security refers to a collection of practices aimed at keeping cyber-attacks at bay. Some measures add extra security layers such that a hacker never finds a way of hacking the code on a website. Others encrypt data so that when cyber-criminals intercept it, they receive irrelevant information.
The secret to a credible website security strategy is continually improving security measures. The AV-TEST Institute registers over 450,000 new malicious programs and potentially unwanted apps every day, so it is safe to assume that the tactics that work today may not work tomorrow.
How do websites get hacked?
Most websites get hacked through a handful of common attacks: malicious scripts, database injections, traffic floods, password guessing and malware.
Hackers have several techniques and motives for attacking your website. While some are after some form of financial gain, others are in it for the fun of cracking a system. Understanding the potential attacks faced by your website helps recognize the safety measures you should take.
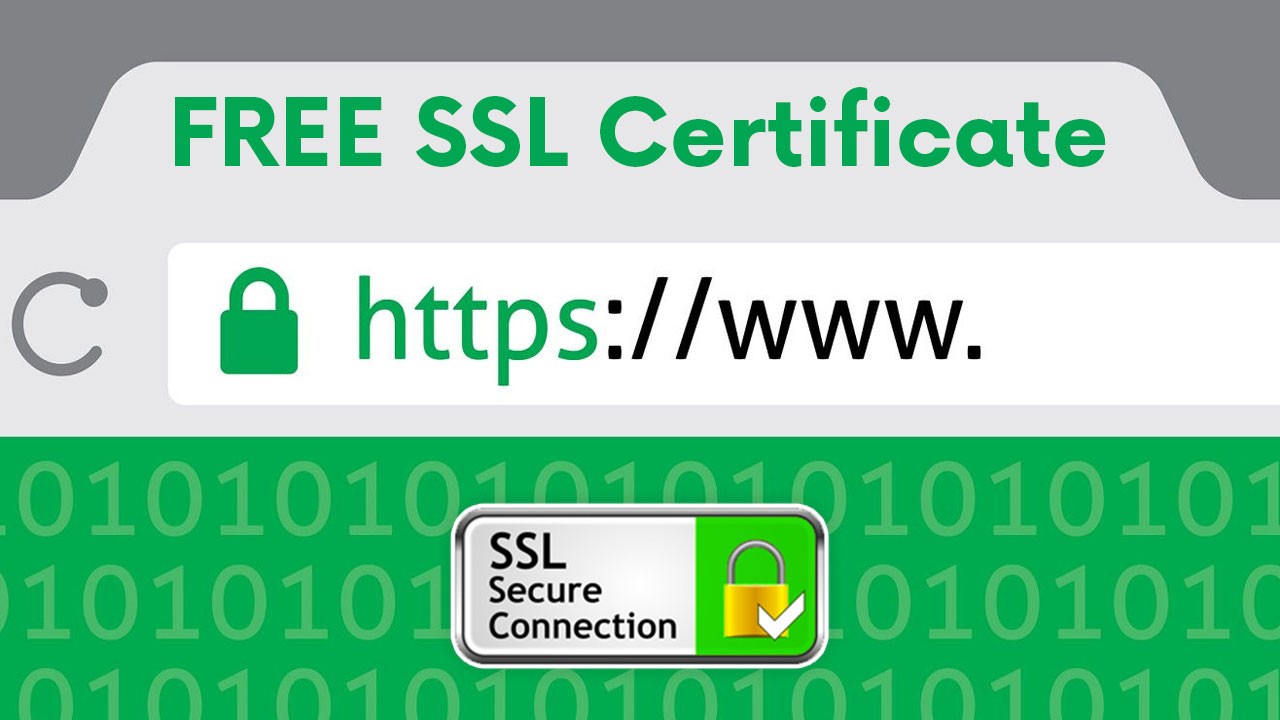
The lock means your site is secured with a valid SSL certificate. (makeawebsitehub.com)
Cross-Site Scripting (XSS)
In a cross-site scripting attack, a hacker places malicious JavaScript code into a site’s database. Planting the code is not hard, since an attacker may inject the code by submitting a non-validated comment on a blog post. Once a user requests a page from your website, they receive the required information together with the attacker’s JavaScript. The user’s browser then executes the injected code.
A hacker may get a user’s cookies through this method and use it to hijack sessions. They can do more damage, such as logging keystrokes and capturing the user’s screen. Worse yet, they can control the user’s computer remotely.
SQL Injections
In database-based websites, users occasionally query the database. A hacker can use a form field to submit a query as a regular user. However, they add malicious code in the SQL command, allowing them to modify database tables. SQL injections are especially easy when users provide search parameters.
After a successful SQL injection, a hacker gains access to confidential information such as your customer’s credit card numbers. Furthermore, they modify, delete, or insert data, compromising the integrity of a database. In the worst-case scenario, they can take over your web server.
DoS/DDoS Attacks
Denial of Service (DoS) attacks take a website down by overwhelming system resources. A hacker can send massive traffic to a server, making it unable to handle other user’s requests. If the attack is a Distributed Denial of Service (DDoS), the malicious actor first infects other hosts and uses them to generate traffic.
The primary purpose of a DDoS attack is to take a website down. It may be that a hacker is doing so for your competitors or just having fun. However, a cyber-criminal may aim to slow the website down to pave the way for another attack.
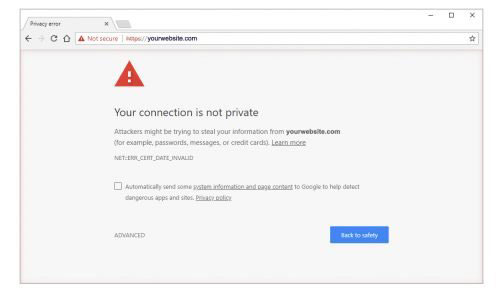
Chrome will oftentimes display this page when a site lacks encryption. (webdesign309.com)
Brute-forcing
Numerous websites, especially those that run a Content Management System (CMS), have a user authentication system. A hacker can try different combinations of usernames and passwords to gain access to a system.
Two major password hacking techniques are brute-forcing and dictionary attacks. In a brute-force attack, a hacker attempts to penetrate a system using random letter combinations. In a dictionary attack, the hacker uses a list of common passwords and tries to find the one matching with the target pass-code.
If successful, a hacker may gain total control of a system. They can take the website offline or use the server to commit cyber-crimes.
Malware Attacks
Hackers can place malicious programs on your server. Of course, they need to gain access to your system using the methods discussed above. The software they upload may infect applications or files.
Successful malware attacks may be especially devastating to website administrators, as stealth viruses are difficult to find. Worse, a hacker may create a backdoor and use your system whenever they want. Also, cyber-criminals may upload malware as downloadable files. Once your website visitors make a download, the hacker takes control of their computers.
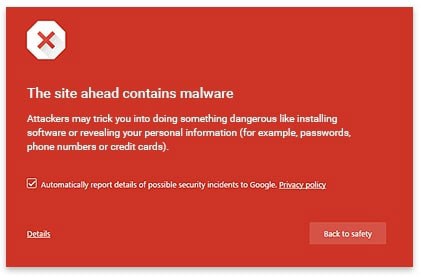
Chrome will oftentimes display this warning if a site contains malware (webinspector.com)
How can you secure your website and protect user data?
You can secure your website with nine practical steps: strong passwords, software updates, an SSL certificate, a firewall, physical security, limited user access, separate hosting, safer default settings and web security tools.
Are edu sites safe? Can someone hack an educational or government website? Well, cyber-criminals can target anyone.
More than they need data, hackers require resources to commit more malicious tasks. Thus, it does not mean much that your website contains no sensitive information. As long as you host it on a server, it is as susceptible to hacking as big websites are. Every website, from big company sites to personal blogs, needs web security.
Luckily, you don’t have to be a computer geek to secure a website. By simply searching for “how secure is a website” on the internet, you can access tools to analyze your site’s security state. If the safety examination reveals vulnerabilities, you have a starting point.
Here is what you need to do to secure your website and protect the information you collect from your site’s visitors.
Use Strong Passwords
Passwords are so common that it is easy to forget what role they play in web security. If your website has an admin dashboard that requires authentication before granting access, ensure the pass-code you use is uncrackable. Additionally, if your site requires users to sign up, put in place measures to ensure that they choose strong passwords. Never store user passwords as plain text or with a fast hash such as SHA-2. The OWASP Password Storage Cheat Sheet recommends a slow password hashing algorithm such as Argon2id or bcrypt instead.
But what is a strong password? The short answer is a long one. The U.S. NIST password guidelines (SP 800-63B) require at least 15 characters for a password used on its own, and at least 8 characters when the password is paired with a second login step, such as a code sent to your phone. A long passphrase is much harder to crack than a short, complicated password.
Skip forced password changes on a schedule. The same NIST guidelines say sites should not make people change passwords periodically, only when there is evidence a password has been compromised. Also, avoid using similar passwords across numerous online accounts. Finally, start using password managers such as LastPass that can help generate and use passwords efficiently.
Keep Your Software Updated
As mentioned, hundreds of thousands of new malware programs appear every day. Hackers are constantly scouting for websites running outdated software with known security vulnerabilities. If your website’s core or dependencies are not the latest versions, then a cyber-criminal will have an easy time hacking it.
If your site runs on a managed host, implementing updates is probably your hosting company’s job. The same applies if you used a website builder to create your site.
However, CMS based sites require you to update the software. Content management systems such as WordPress release regular updates of their core. Also, there are many new versions of plugins and themes associated with your WordPress installation. Developers using frameworks should also check on available updates.
There are a variety of ways to more easily perform software update tasks. For example, you can use plugins that email you once an update is available. Further, you may use tools that notify you of new vulnerabilities in software in use on the site.
It is essential to understand that software updates usually fix known system vulnerabilities. Failure to install updates allows malicious bots to easily attack your site.
Install an SSL Certificate
If you have been wondering what technology provides secure access to websites, SSL may be the answer. A Secure Sockets Layer certificate powers encrypted sites. The certificate lets the browser scramble the data a user enters into a string of unreadable characters. The certificate also helps confirm that the user’s requests go to the right server.
But are secure sites safe? SSL does not make hacking your website impossible. An attacker may still intercept data sent between your web server and your site’s visitors, even with an expensive certificate. However, even if the hacker gets a hold of the data, it is all encrypted. Therefore, they cannot use it to harm anyone.
Some web hosts allow you to install the SSL certificate free of charge. However, advanced certificates, usually appropriate for e-commerce websites, require you to pay. If you need a regular certificate and your budget is low, check out Let’s Encrypt, a certificate authority that provides free TLS certificates.
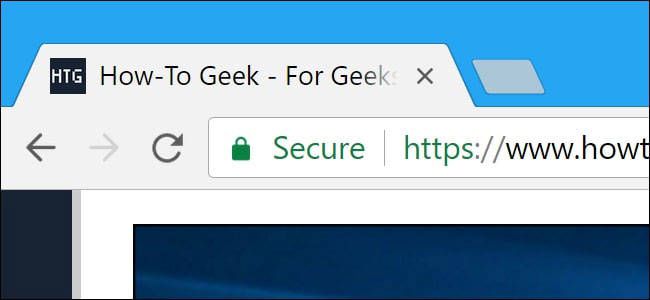
SSL certificate and HTTPS prefix (howtogeek.com)
Use a Web Application Firewall (WAF)
A web application firewall (WAF) is one of the easiest and most direct ways to increase a website’s security. A WAF adds a protective layer that a malicious actor must bypass in order to hack your website. Since WAFs filter HTTP traffic, they can prevent multiple attacks, including XSS, SQL injections, and DDoS attacks.
While at it, you can install other anti-malware software. For example, it would be great to have a website scanner that examines your site for malware’s possible existence in the web server directories. The software may delete or rename infected files such that a hacker is unable to use them.
Enforce Physical Security
Do you host your website on personal servers? Well, you need to keep it secure, physically. Keep tabs on people who come in contact with the server. A good practice is to keep the server locked in a room that only a few select people can access.
If you happen to be using a web host, keep your personal computer (PC) safe. Avoid lending out your PC or using public Wi-Fi networks such as those in airports. Moreover, regularly scan the PC you use to access the control panel, and seek out any potential viruses. If you find a file that you do not recognize, installing it may be dangerous. On the contrary, deleting it may help keep hackers off your website.
Manage User Access
Granting all website users the permission to read, write, and execute commands is a recipe for easy hacking. As an administrator, you should be the only one with full permission. However, other users can have the access level necessary for them to do their jobs. In short, implement the Principle of Least Privilege.
Security systems should also monitor what users do once in the system. Be sure to keep a record of tasks performed by guests so that tracing a potential hacker is easy.
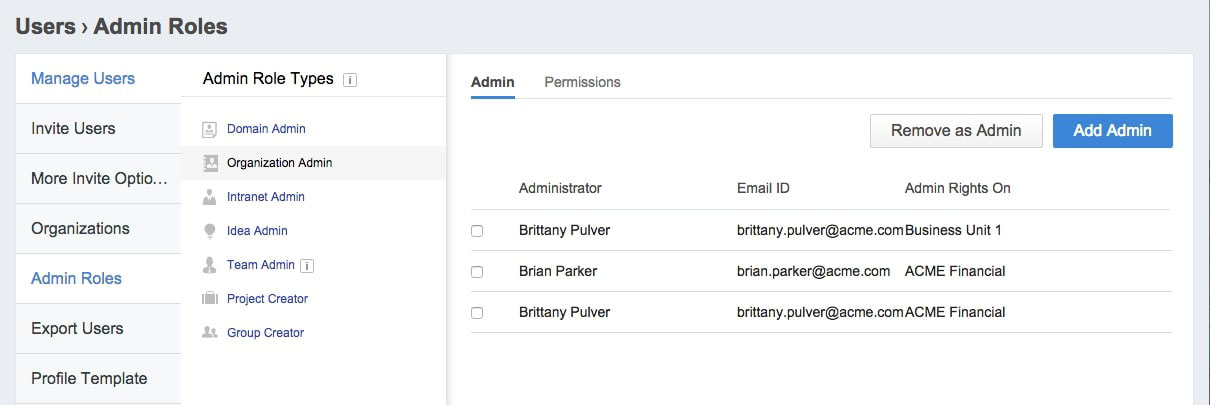
Applications such as Mangoapps can help you manage your users and administrators(mangoapps.com)
If need be, limit the amount of time a user has permission to carry out certain tasks. For instance, delete tokens that allow users to change passwords after a short period. Short time limits reduce the damage a cyber-criminal can do.
Host Different Sites Separately
It may be tempting to host all sites on a single server, especially if your hosting plan allows unlimited websites. From a security point of view, putting every site on one server is poor practice. All you have is a single root directory with multiple folders. Thus, if a hacker gets into the server, then they can compromise every site on it.
Unfortunately, the safest way to stop an attack from spreading between sites costs more money. It would help if you hosted every website on a dedicated or virtual server. With a reduced attack surface, it becomes easier to keep hackers off a website.
Check on Default Settings
Configurations may be either technical or non-technical. The less tech-savvy side is that presented by the dashboard. You should double-check default settings and change them if necessary. It would be unwise to maintain a setting that gives administrators privileges to all users.
Technical configurations may require the help of a web security expert to tweak. Technical changes involve examining web server configurations. After locating the configuration file, go over it and understand the rules. You may modify them accordingly if you wish to, for example, modify file names after uploads.
Start Using Web Security Tools
There are tons of useful resources dedicated to keeping your website safe. Some happen to be free, while others have a price tag. They help you with essential tasks, including:
- Performing security audits such as tests on XSS and SQL injections
- Scanning your site for malware
- Monitoring your speed
- Automating security updates
- Generating security reports
- Backing up your site
Checking that the tool you are using is from a reputable developer should always be a priority.
Did you know? An SSL certificate shows visitors a padlock in the address bar, and browsers such as Chrome warn people when a page is not secure.
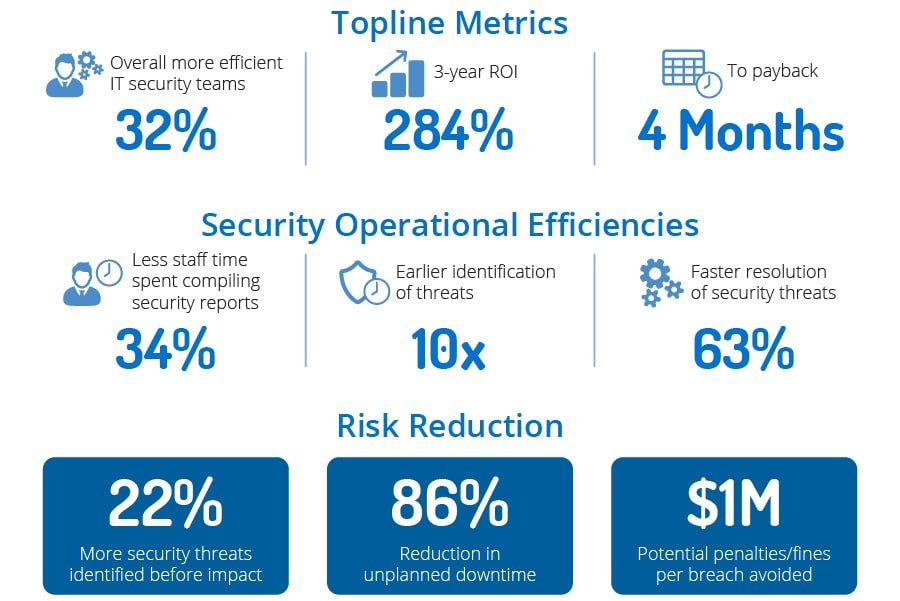
Web security tools can be great to assess the security status of your website. (recordedfuture.com)
What should you do after your website is hacked?
After a hack, change every password, back up your site and logs, get expert help to clean it, tell the people affected, check your own devices and then restore a clean backup.
While keeping the risk of a website hack at a minimum is possible, lowering it to zero may not be achievable. Do you have a good answer to what an encrypted website is? Have you begun encrypting your site and implementing other safety measures? Even after securing your site, cyber-criminals may still be able to hack it.
If you happen to be a victim, there are a few steps you can take to sustain the availability and integrity of your website. The main steps are:
- Change passwords: As soon as you realize that someone hacked your website, change every password associated with the site. You need to set new FTPS, database, and app pass-codes.
- Create a backup: Even if you think that malware still exists among the files, it is important to backup your site. Remember to create copies of server logs, which help with investigations.
- Consult a website security specialist: While there is software to remove hacks, it is best to hire an expert to do away with injected malware. Other than eliminating viruses, a professional can identify and get rid of backdoors.
- Notify affected parties: In some regions such as Europe, the law requires that you tell all affected people about the hack. Regardless of legal provisions, it is helpful to be open about website hacks so that your customers know about compromised information.
- Check personal security: Examine your PC and any other personal device used to access the hacked website.
- Restore backup: Once the server is clean, restore a backup from periods before the hack and get your website back online.
What are the most common website security questions?
The most common website security questions cover encrypted websites, edu sites, how safe secure sites are, the technology behind secure access and the risks a website faces.
Do you have some questions about the security of your website? Review the answers below before commencing an in-depth search.
What is an encrypted website?
Encrypted sites are those with a valid SSL certificate. Their URL features an HTTPS prefix, and they usually have a lock on the address bar.
Are edu sites safe?
Websites with an edu TLD (Top Level Domain) belong to academic institutions. They usually contain credible information but are not immune to hacking.
Are secure sites safe?
A secure site has a web application firewall to prevent several hacking techniques, such as XSS. While no site is truly unhackable, a secured website has the least chance of getting hacked.
What technology provides secure access to websites?
A protocol called Transport Layer Security (TLS) is the current technology securing websites. Most people still call TLS by the name of its predecessor, SSL.
What risks does a website face?
Several hacking risks against websites exist. Hackers can take a site down, deface it, and steal sensitive data from the website database, among other malicious actions.
Did you know? Google says HTTPS is part of a good page experience, but beyond Core Web Vitals, page experience factors don’t directly help your website rank higher. Install SSL to protect your visitors, not to chase rankings.
Why should web security be a priority?
Web security should be a priority because a hacked website can cost you customer trust, sales and your reputation.
A website is only as good as its security. By maintaining the integrity of a site, security can help preserve the reputation of a business. Without online safety, customers may choose against dealing with online sellers, which ultimately translates to lost revenues.
Web safety starts with your understanding that security is a journey and not a destination. You can start by using affordable tools to examine the security of your website. Afterward, you may implement simple measures such as using strong passwords and work your way up. The sound advice of a professional web security expert can help you a great deal.
How can diib help keep your website healthy?
diib gives you a dashboard of your website’s health and search data, with plain-English recommendations on what to fix next.
Security is one part of a healthy website. diib helps you keep an eye on the rest, from your traffic to how your site shows up in search.
With diib, you get:
- Plain-English recommendations on what to fix next
- Alerts when something important on your site changes
- Managed SEO, which recommends the technical fixes your site needs
- A dashboard with your website and search stats in one place
diib members can also join diibLive office hours with our growth experts. Click here for our free 60 second site scan today!
FAQ’s
A Secure Sockets Layer (SSL) certificate, which today uses Transport Layer Security (TLS), encrypts the data moving between your visitors and your web server. If a hacker intercepts that data, they see only unreadable characters. The certificate also helps confirm that requests reach the right server, and browsers show it as HTTPS with a padlock.
Some web hosts let you install a Secure Sockets Layer (SSL) certificate free of charge, so check with your host first. If your budget is low, Let’s Encrypt is a certificate authority that provides free TLS certificates. Advanced certificates, usually suited to e-commerce websites, cost money.
HTTP sends data between a visitor’s browser and your website without encryption, so anyone who intercepts it can read it. HTTPS means the site has a valid SSL/TLS certificate and encrypts that data, so intercepted information is unreadable. Browsers such as Chrome show a padlock on HTTPS pages and warn people when a page is not secure.
An SSL certificate does not make your website impossible to hack. Attackers can still get in through weak passwords, outdated software or other security gaps, and they may still intercept data in transit. What the certificate does is keep that intercepted data encrypted, so hackers cannot read it or use it to harm your visitors.
A website can load without HTTPS, but any site that collects passwords, payments or personal details should use it. Browsers such as Chrome warn visitors when a page is not secure, and Google treats HTTPS as part of a good page experience. Install an SSL/TLS certificate to protect your visitors, not to chase rankings.